
Branch networks
Retail, distribution, financial services and healthcare organisations with many small sites and a few critical applications.

SD-WAN (software-defined wide area network) connects your offices, branches, campuses or clinics over fibre, LTE and 5G, and steers each application down the best available link under central policy. Arke Technologies designs, deploys and manages SD-WAN across South Africa from Johannesburg, and gives you a straight MPLS vs SD-WAN comparison first.
Start with the WAN. A wide area network connects sites that are far apart: head office, branches, data centres and cloud services. That is the WAN defined in one sentence, and the WAN description most buyers recognise is the set of lines and routers that link their offices. The traditional WAN technologies are leased lines, MPLS circuits from a carrier and site-to-site VPNs over the internet.
SD-WAN stands for software-defined wide area network. That is the full form; it is also written SD WAN or SDWAN, and the meaning is in the first two words. An SD-WAN builds encrypted tunnels over whatever links each site has, whether fibre, LTE, 5G or MPLS, and a central controller decides, application by application, which path each flow takes, based on live measurements of delay, jitter and packet loss. When a link degrades, calls and critical applications move to a healthy one without anyone having to notice first.
Put another way, SD-WAN applies the ideas of software-defined networking (SDN) to the WAN network, separating the control plane, where policy is decided, from the data plane at each site. The purpose of SD-WAN is better application performance and resilience over more varied links, with one place to manage every site. It is sometimes marketed as WAN 2.0, but it is less a new network than a smarter way to run the WAN connectivity you already buy. For a longer explanation, read what is SD-WAN.
MPLS (multiprotocol label switching) is a private network a carrier runs for you, with performance guarantees end to end. SD-WAN runs over any mix of links and makes up for the absence of guarantees by using more than one path. The comparison:
| MPLS | SD-WAN | |
|---|---|---|
| Underlay | One carrier's private circuits | Any mix of business fibre, LTE, 5G and MPLS |
| Performance | Carrier SLA on latency, with priority for voice | Measured per link, with traffic steered to the best path |
| Resilience | Depends on the carrier; a second circuit is a second full cost | Two or more links from different networks at each site |
| Cloud access | Backhauled through head office or a hub | Direct, firewalled breakout to Microsoft 365, AWS and Azure |
| Security | Private, but unencrypted by default | Encrypted tunnels, with a firewall needed at each edge |
| Adding a site | Waits on carrier provisioning | As soon as any fibre or LTE link is live |
| Visibility | Carrier reports | Per-application dashboards you control |
| Contract | Multi-year terms with one carrier | Device licences, with links from any provider |
So which is better, SD-WAN or MPLS? For most South African organisations whose applications now live in the cloud, SD-WAN over business fibre and LTE gives more bandwidth, better resilience and direct cloud access. MPLS still earns its place where a single application needs guaranteed latency end to end, or where a contract has years to run. Many organisations therefore run a hybrid SD-WAN, with SD-WAN over MPLS and broadband together, keeping the MPLS circuit at the sites that need it and retiring it elsewhere as contracts end.

SD-WAN is used wherever an organisation has several sites that depend on central or cloud systems, and it is the site-to-site layer of our network infrastructure services. It suits:
Retail, distribution, financial services and healthcare organisations with many small sites and a few critical applications.
Satellite offices, libraries, clinics and pay points connected to billing, finance and records systems.
Campuses sharing student systems, learning platforms and one internet policy. See IT for higher education.
Remote sites where fibre is not always available and LTE or 5G carries the load.
Some platforms extend SD-WAN for home offices with a small edge device or client software; for most staff, a remote-access VPN or a cloud security service does the job.
Load-shedding adds a local reason. When a fibre link drops during an extended outage, SD-WAN moves traffic to an LTE or 5G link from another network, and critical work continues, provided the site cabinet is on a UPS.
The SD-WAN security benefits are practical: every link between sites is encrypted, traffic can be segmented by department or application, policy is set once and pushed to every site, and security-led platforms build a next generation firewall into each edge device. Direct internet breakout is only safe if every site is firewalled; see firewalls and network security.
SASE (secure access service edge) combines SD-WAN with cloud-delivered security: secure web gateways, zero-trust access for remote users, cloud access security and firewall as a service. That raises a common question: is SD-WAN obsolete? No. SASE SD-WAN is still SD-WAN; part of the security moves into the cloud, but every site still needs an edge that chooses paths and holds tunnels. We design today's SD-WAN so that a later move to SASE security does not force a redesign.
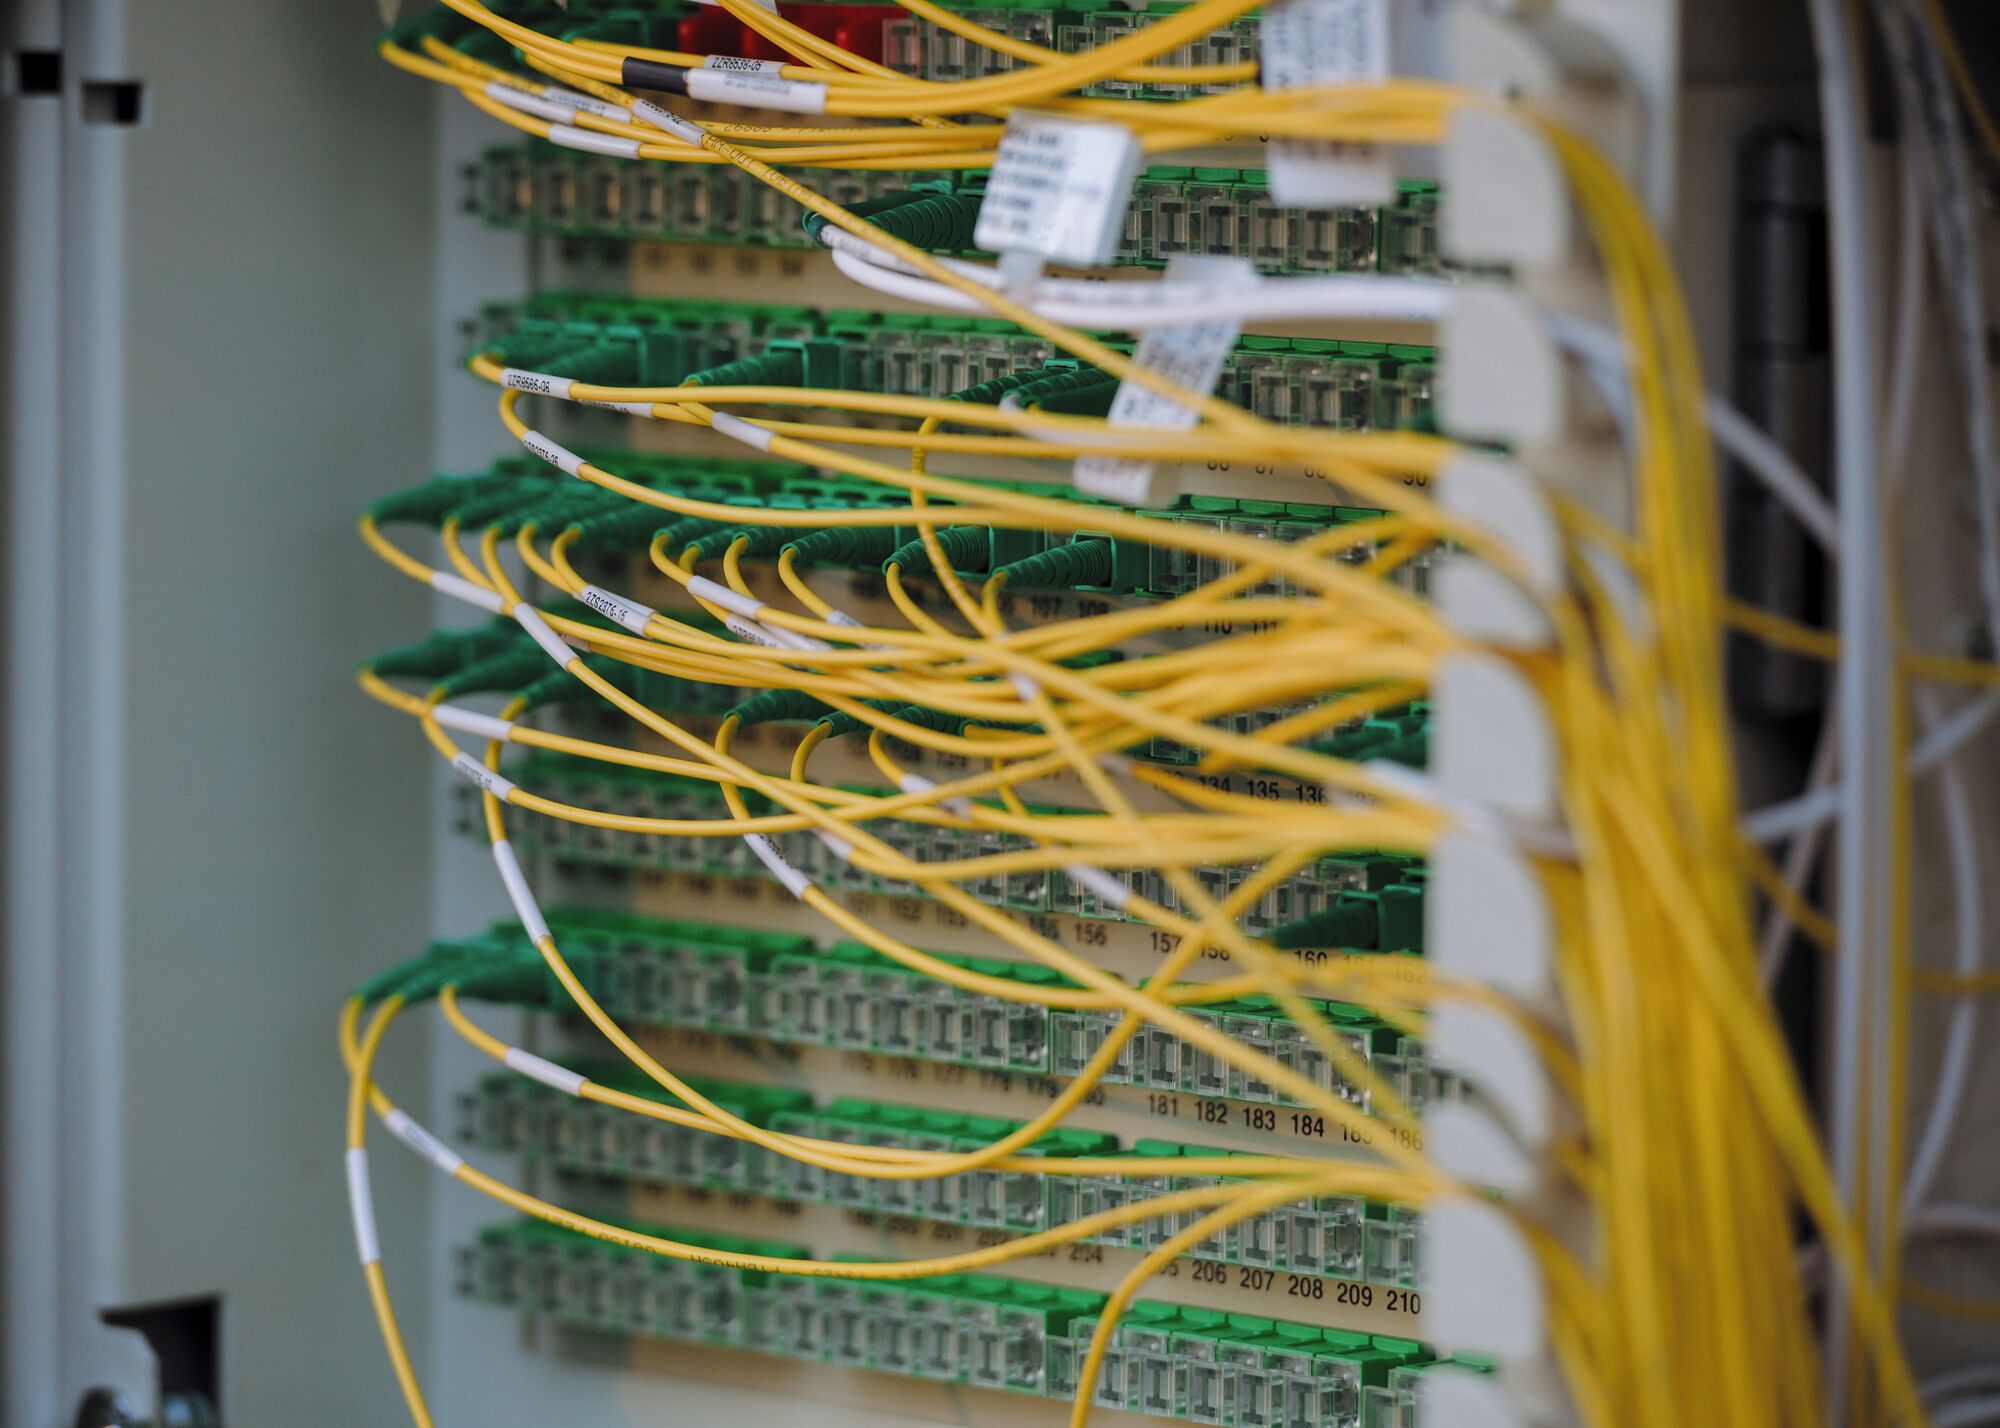
SD-WAN solutions fall into a few families. We configure Fortinet, Cisco, Sophos, MikroTik, Ubiquiti UniFi and TP-Link Omada equipment (experience, not partner status), and we recommend the family that fits your sites:
01.
We map every site, its links, its applications and its traffic, and read your existing WAN contracts for notice periods.
02.
Ideally two links per site from different networks: business fibre plus LTE or 5G. Fibre Boyz, our connectivity division, can supply business fibre and LTE, so one supplier carries the whole stack; see business connectivity.
03.
Topology (hub-and-spoke or mesh), application policies for voice, Microsoft 365 and line-of-business systems, security zones and failover behaviour.
04.
One or two sites first, with failover tested by disconnecting each link in turn.
05.
Edge devices are supplied through Server Hub and configured before dispatch; where the platform supports zero-touch provisioning, a site comes online once its device is connected. Each site needs clean structured cabling, power and, where staff roam, sound business Wi-Fi.
06.
Link quality, firmware, licence renewals and change control, with a monthly service review showing performance per site and per link, backed by network monitoring.
Last reviewed: September 2026
We quote the rollout as a project after an assessment, and ongoing management inside a managed service agreement. What drives the cost of each option:
The comparison that matters is total cost over the term, including the second link each site needs. We model MPLS and SD-WAN side by side for your estate before you decide.
SD-WAN is the better fit for most organisations whose applications run in the cloud, because it combines several affordable links, steers traffic to the healthiest one and breaks out directly to cloud services. MPLS remains the better choice where one application needs guaranteed latency end to end. Many organisations run both for a while, using SD-WAN over MPLS and broadband until MPLS contracts end.
An SD-WAN is used to connect several sites to each other and to cloud services over a mix of links, with central control over which traffic takes which path. Typical uses are branch and campus connectivity, keeping voice and video calls clear, failing over to LTE or 5G when fibre drops, and applying one security policy across every site.
SD-WAN is not obsolete; it has become the network half of SASE (secure access service edge). SASE adds cloud-delivered security, such as secure web gateways and zero-trust access, but every site still needs an edge device that holds tunnels and chooses paths. A well-designed SD-WAN can adopt SASE security later without a redesign of the sites.
SD-WAN is better than a traditional WAN mainly because it uses every link a site has instead of leaving backups idle. It measures each link continuously, sends critical traffic down the best one, encrypts everything between sites and is managed from one console. Adding a site is faster, and cloud applications no longer travel through head office first.
Five common disadvantages of a traditional WAN are cost, because private circuits are expensive for the bandwidth; complexity, because many sites and devices must be configured; security exposure, because every link is a way in; performance, with delay over distance and congestion; and dependence on carriers for changes and repairs. SD-WAN reduces most of these, though it still needs good design and management.
Organisations with several sites use SD-WAN: retailers, distributors, banks and insurers with branches, healthcare groups, mining companies, and public bodies such as municipalities and provincial departments. Colleges and school groups with more than one campus use it too. The common thread is several locations that depend on central or cloud systems, where an outage at one site stops real work.
Yes, SD-WAN works well with 5G and LTE, which are common second links at South African sites and the only links at some remote ones. A 5G SD-WAN design uses the mobile link as a full path rather than an idle backup, with data limits and cost controls set in policy. We recommend a mobile link on a different network from the site's fibre.
Send us your site list and current WAN contracts, and we will set out MPLS vs SD-WAN for your estate, with costs over the term.