010 447 2445Contact
Arke Technologies home
An IT manager takes a call at his laptop in a glass-walled office.

Managed security operations for organisations in South Africa

Managed security operations is the ongoing work of hardening, monitoring and governing an organisation's systems. Our team at Arke Technologies (Pty) Ltd runs it for several client organisations in South Africa, covering Microsoft 365 hardening, Microsoft Sentinel SIEM, Entra ID governance, Linux server administration and POPIA compliance.

The engagement at a glance

ItemDetail
ServiceOngoing managed IT and cybersecurity
ClientsSeveral client organisations, referenced in general terms
CountriesSouth Africa
PlatformsMicrosoft 365, Microsoft Sentinel, Entra ID, AlmaLinux servers, cPanel web hosting
GovernanceA service-level agreement per client, with a monthly service review and report
DeliveryRemote-first, on our own tooling, from our Johannesburg head office
Outcome we can shareA system our team delivered for one of these clients two years ago still runs without issues

We name no clients: security work is confidential, so we describe it in general terms and share more only where the organisation concerned has agreed. This case study, part of our work, shows our cybersecurity services as they run day to day.

What the managed security operations cover

Hands on a laptop keyboard beside a phone, ready for a sign-in prompt.

How the service runs

The work follows the four phases of our managed IT services method:

  1. Discovery

    We document the estate: users, devices, tenants, servers, administrator accounts and the data that falls under POPIA.

  2. Baseline

    We set the security baseline for Microsoft 365, Entra ID and the servers, agree it with the client and record every deviation.

  3. Management

    We run the environment day to day: monitoring, patching, access changes, incidents and requests, all against the SLA.

  4. Optimisation

    Each monthly service review looks at incidents, open risks and changes, and sets the next improvements.

The work runs on our own tooling. Remote access goes through our own platform, built on open-source RustDesk with a management system we own, on our own Johannesburg servers, and every remote session is approved and logged. Monitoring checks each computer every 15 minutes and logs faults as tickets automatically. Standard repairs come from a library, and the riskier ones need a recorded human approval before they run. Read more in RustDesk for business. We are building the same pattern into Hesper, our IT operations platform, which launches in November 2026.

Monitoring is automated; people act to the SLA

We are precise about what is automated and what is not. Monitoring raises tickets on its own; people then act on each incident by its priority on a P1 to P4 scale, from a P1 critical outage to a P4 low-impact request, with targets matched to the business impact of downtime and agreed, with the cover hours, in each client's SLA.

This is not a staffed, round-the-clock security operations centre, and we do not describe it as one. If your risk profile calls for an always-staffed centre, ask any provider who is watching at 02:00 and check the answer against the contract.

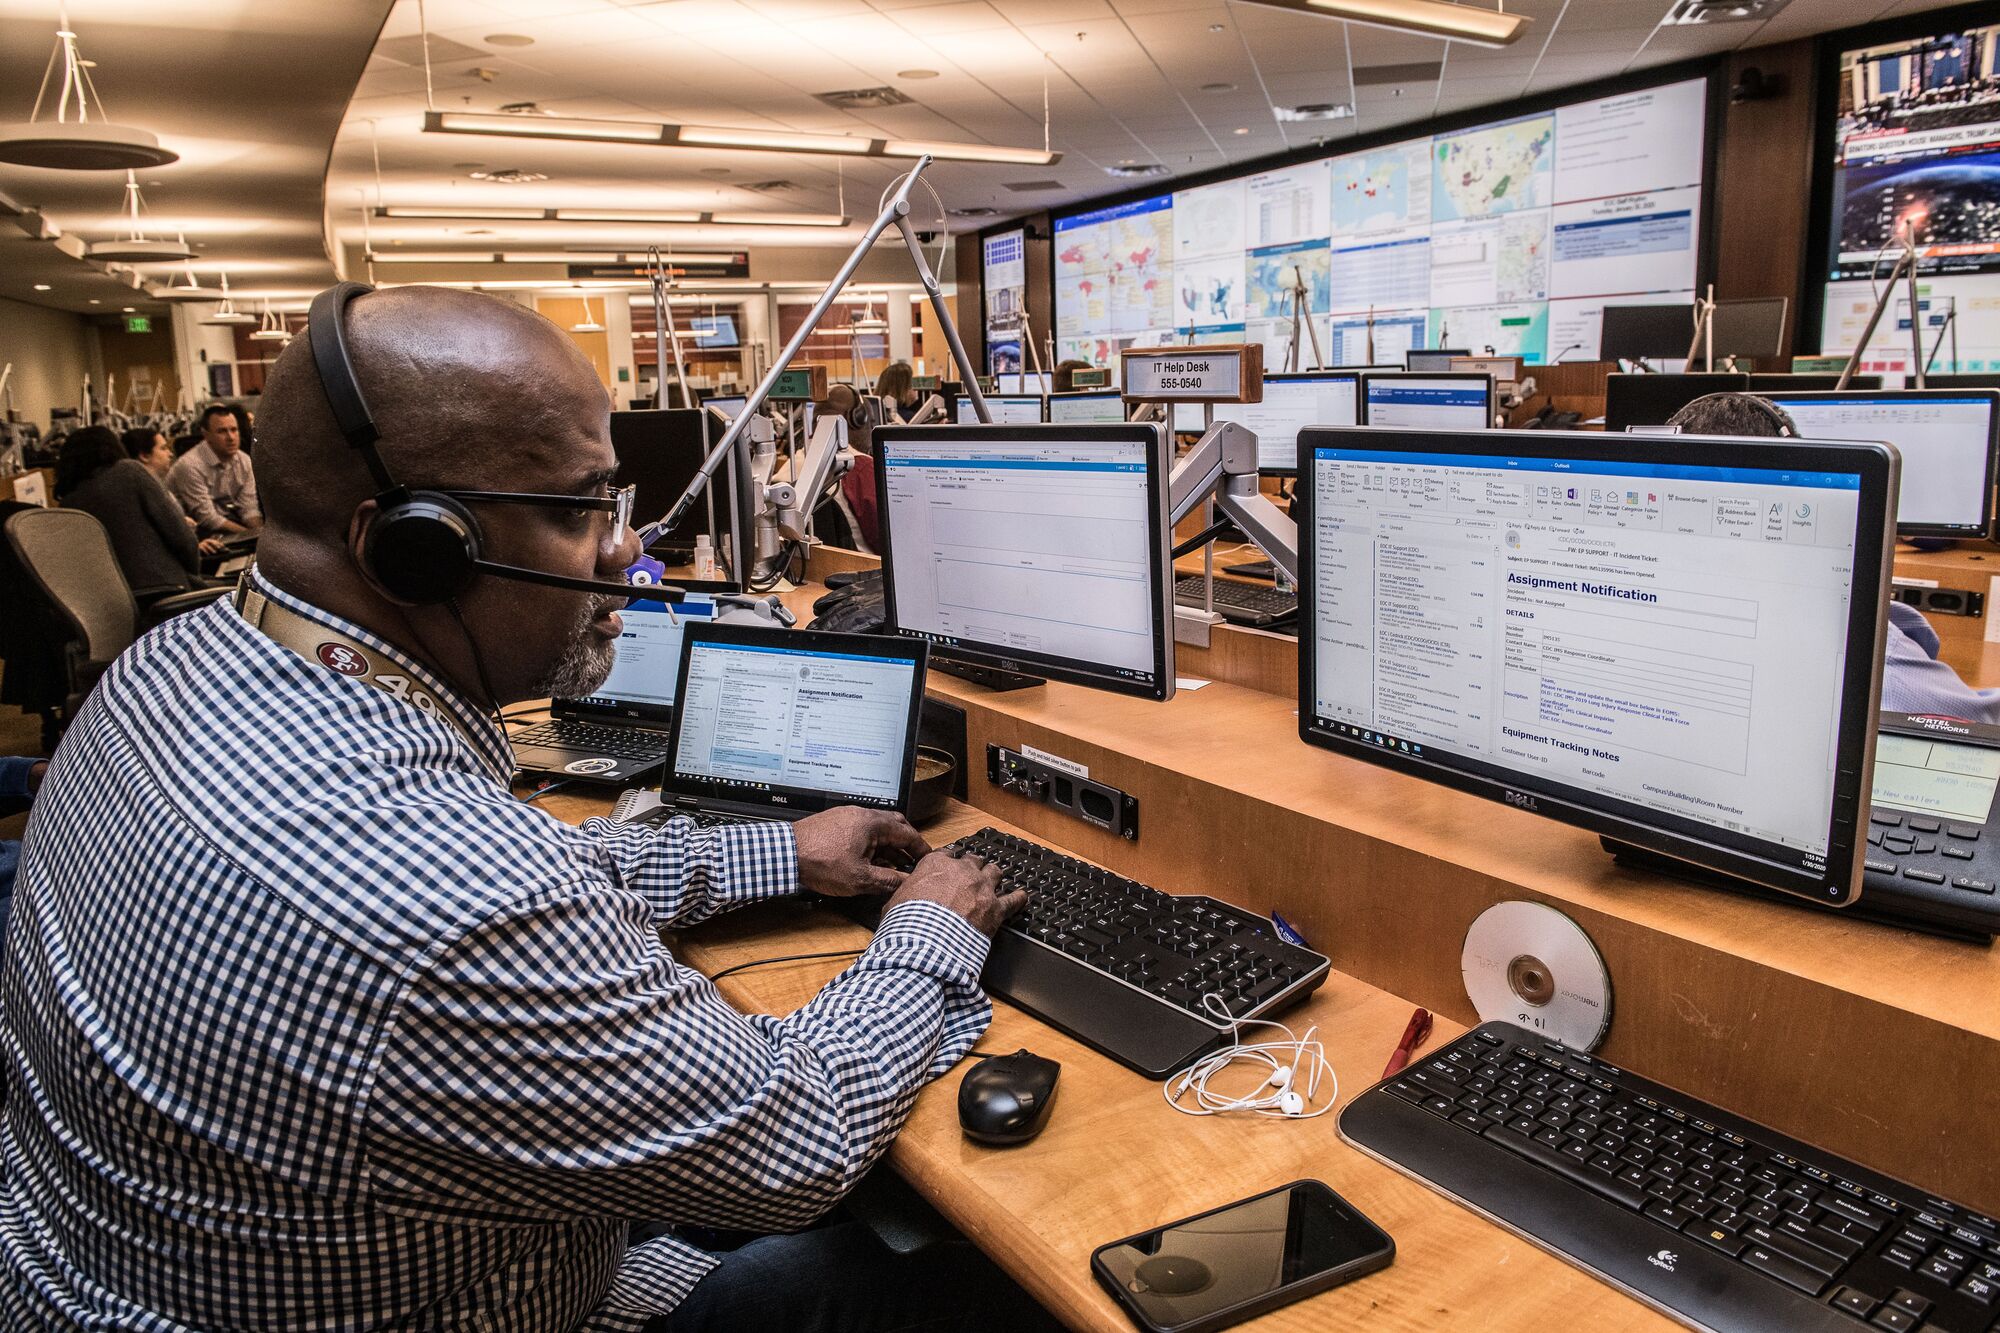
An operations analyst in a headset works across several monitors in a busy operations room.

Governance and reporting

  • Monthly service review and report for every client, covering incidents, changes and open risks.
  • ITIL-aligned practice for incidents, requests, problems and changes, with escalation paths, change control and documented runbooks.
  • Evidence for the board. King IV Principle 12 expects boards to govern technology and information. The baseline, the access reviews and the monthly reports give directors evidence rather than assurances. See IT governance, risk and compliance.
  • Frameworks we work to. Controls aligned with the NIST Cybersecurity Framework, CIS Controls and ISO/IEC 27001, so a client working towards certification starts with evidence already in place. See ISO 27001 readiness.

Buying managed security from Arke

  • How it is priced. Per user per month, set after an assessment, with project work outside the SLA quoted separately. We publish no seat prices or rates. Last reviewed: September 2026.
  • How to buy. A proposal, an SLA and a purchase order, or a tender response in which we complete the standard bidding documents (SBD forms).
  • Procurement documents. Level 1 B-BBEE contributor (sworn affidavit available on request), giving 135% procurement recognition; company documents, CSD supplier number and SARS tax compliance status available on request.
  • Exit and handover. You own your data, credentials and documentation. At exit we hand over administrative access, the baseline and the runbooks, and remove our tooling.

Frequently asked questions

What are managed security operations? Show answer

Managed security operations are the continuing work of keeping an organisation's systems hardened, monitored and governed, carried out by an outside team under a service-level agreement. For the clients in this case study, that meant Microsoft 365 hardening, Microsoft Sentinel as the SIEM, Entra ID governance, Linux server administration and POPIA compliance management, reviewed and reported every month.

Is your security monitoring staffed around the clock? Show answer

No, and we do not claim it is. Monitoring is automated and continuous: it checks each computer every 15 minutes and logs faults as tickets automatically. People then act on each incident according to its P1 to P4 priority and the cover hours and targets agreed in your SLA, which are set to the business impact of downtime.

What does Microsoft Sentinel do? Show answer

Microsoft Sentinel is Microsoft's cloud-based SIEM: it collects sign-in, audit and security logs from Microsoft 365, Entra ID, servers and other sources into one workspace, and raises incidents when activity matches a suspicious pattern. Its value depends on which logs you connect and how the resulting incidents are handled, which is why we tie them to the SLA.

How much do managed security services cost in South Africa? Show answer

Published South African managed IT rates run from about R180 to R400 per user per month (matnet.co.za, September 2026), with some providers listing R450 (MiBOT, September 2026), and security scope adds to that. We price per user per month after an assessment. The main drivers are users, servers, the log volume Sentinel ingests, which Microsoft charges for, and compliance work.

What happens to our systems if we leave? Show answer

You keep everything. Your data, credentials and documentation are yours throughout the contract, and at exit we hand over administrative access, the security baseline and the runbooks, then remove our remote-access and monitoring tooling. We plan the handover so that your next provider or in-house team starts from a documented environment rather than a blank page.

Know where your security stands

We start with an assessment of your Microsoft 365 tenant, identities and servers, and a written report of what to fix first. Read how our cybersecurity assessment and audit works, then ask us to scope yours, email info@arketechnologies.com or call 010 447 2445.